Certifications and Career Paths

Who is this Research for:

  • Beginners exploring a career in cybersecurity
  • IT professionals transitioning into security roles
  • Students researching cybersecurity certifications
  • Professionals comparing credentials and security domains
  • Aspiring SOC analysts, blue team members, security professionals
  • Entry-level ethical hackers and penetration testing students
  • Cloud engineers learning security fundamentals (AWS, Azure, GCP)
  • Career changers evaluating cybersecurity
  • Professionals preparing for Security+, CySA+, CEH, CISSP, or OSCP
  • Business owners who need practical security awareness
  • Anyone curious about cybercrime and digital threats

Cybersecurity Career Paths List: 

  • Security Analyst
  • SOC Analyst
  • Penetration Tester
  • Digital Forensics Investigator
  • Cloud Security Engineer
  • GRC (Governance, Risk & Compliance)
  • Cybercrime Investigator
  • Incident Response Analyst
  • Threat Intelligence Analyst
  • Application Security Engineer (AppSec)
  • Security Engineer
  • Red Team / Blue Team Specialist
  • Security Architect
  • CISO / Security Leadership

Entry-Level Certifications:

  • A+ (Core IT support & troubleshooting)
  • CompTIA Security+
  • Network+
  • ITF+
  • CySA+ (Cybersecurity Analyst)
  • PenTest+ (Penetration Testing)
  • CASP+ (Advanced Security Practitioner)
  • DataSys+
  • AI Essentials

Intermediate & Advanced Certifications:

  • CISSP – Certified Information Systems Security Professional
  • OSCP – Offensive Security Certified Professional
  • CISM – Certified Information Security Manager
  • CASP+ – CompTIA Advanced Security Practitioner

Cybersecurity Uncovered:

Cybersecurity analyst examining AI model activity and command logs on two monitors.

Hidden AI Backdoors: Risks and Defenses

Hidden AI Backdoors: When a Trusted Model Becomes a Security Risk An AI assistant can answer questions correctly, handle routine work, and still carry a hidden instruction that changes its behavior under specific conditions. That possibility sits at the center of the supplied transcript of Security Now, episode 1100, recorded October 13, 2026. During the episode, Steve Gibson and Leo Laporte discussed malicious modifications to large language models (LLMs). The practical question reaches beyond whether an assistant produces a good answer: what happens when that assistant also has permission to read files, run commands, or contact outside systems?
Read More »
Gitleaks secret scanning

Gitleaks: Find Exposed API Keys, Passwords & Tokens

Gitleaks: Finding Exposed Credentials Before They Become a Bigger Problem A website project can contain more than code. It may also contain the credentials that let that code send email, connect to a database, or access a paid service. During development, copying a working key into a configuration file can feel convenient. The trouble begins when that file becomes part of a shared project. Gitleaks helps identify those mistakes. It is an open-source command-line tool that looks for potential secrets, including passwords, application programming interface (API) keys, and tokens, in Git repositories and files. An API key is

Read More »
SOC analyst reviewing security alerts and event logs at a dual-monitor workstation

What Does a SOC Analyst Do During a Shift?

What Does a SOC Analyst Actually Do During a Shift? A suspicious login appears on a screen. An employee reports an unusual email. A security tool flags a program running on a company laptop. Which one needs attention first—and what would justify taking action? Those decisions are central to a SOC analyst’s job. SOC stands for Security Operations Center, a function that brings together people, processes, and technology to monitor and respond to security threats. The analyst helps turn security signals into an explanation of what happened and what the organization should do next. A shift can include

Read More »
The Dark Stories Series

The Server That Remembered Tomorrow

The Dark Stories Series The photograph showed Maya entering the freight office at 8:17 the following morning. She stood beneath the broken security light, one hand raised against the rain. Her yellow tool bag hung from her shoulder. Behind her, reflected in the glass door, a white pickup waited with its headlights off. Maya checked her phone. Tuesday. 6:42 p.m. According to the file, the photograph would not be taken for another thirteen hours. She enlarged it until the face dissolved into squares. Then someone tried the office door. “Still working?” Rafael called. She closed the window. “Almost

Read More »
The Dark Stories Series

The Room Between Words

A Dark Stories original The woman outside Justin’s apartment had been knocking for eleven minutes when he recognized her voice. “Justin. Please open the door.” He sat on the kitchen floor with his headphones clamped over his ears. On his laptop, the same sentence waited beneath a thin white cursor. He played it again. “Justin. Please open the door.” Same breath. Same tremor. Even the small click of her tongue before his name. The recording was nineteen years old. Outside, the woman stopped knocking. “I know you found me.” Three days earlier, Justin Vale had been worried about

Read More »
The Dark Stories Series

Ghost in the Firewall

At fourteen, Elias Vale thought the greatest challenge was getting through a locked door. Years later, he would learn that keeping the world’s doors closed was far more difficult. At fourteen, Elias Vale had already learned that every locked door had a weakness. Some doors were made of steel. Others were made of code. The dangerous ones were guarded by people who believed they were impossible to open. Elias lived in a cramped house at the edge of a quiet American town, where nobody knew that the pale kid who barely spoke at school spent his nights slipping

Read More »
Is-Cybersecurity-Hard-to-Learn

Is Cybersecurity Hard to Learn?

Is Cybersecurity Hard to Learn, Here’s What the Evidence Shows Cybersecurity can feel intimidating. Strange terms, complicated tools, and endless course choices make getting started seem harder than it should be. But learning the basics and mastering advanced security work are different challenges. Nathan House of StationX draws on a reported 30 years in cybersecurity and more than 500,000 students. His central message staying focused can be a bigger obstacle than understanding the lessons. That’s an educator’s observation, not a study tracking 500,000 learners. What’s easier Start with concrete ideas recognizing suspicious emails, understanding account permissions, and learning

Read More »
Can-AI-Agents-Handle-Real-Cybersecurity-Challenges

Can AI Agents Handle Real Cybersecurity Challenges?

An impressive AI demonstration can grab your attention. A realistic test asks a tougher question: what happens when the easy approach fails? That’s the idea behind zSecurity’s experiment comparing OpenClaw, Hermes Agent, and Agent Zero against four targets with different levels of difficulty. The hardest challenge required linking multiple security weaknesses together to achieve remote code execution—making a target computer run commands remotely. According to the creator, the agents approached the challenges differently. Some emphasized speed and familiar patterns. Others adjusted their approach when an initial attempt failed. That distinction matters. Finding an obvious weakness is one thing.

Read More »
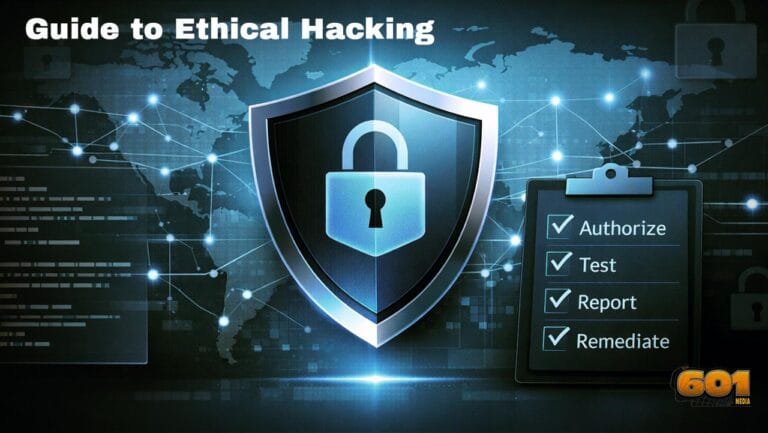
Guide to Ethical Hacking

Guide to Ethical Hacking

Guide to Ethical Hacking: How Legal Penetration Testing Actually Works Ethical hacking is the disciplined practice of finding security weaknesses with explicit permission, then translating those findings into fixes a business can ship. This guide walks through the real workflow—authorization, scoping, recon, testing, exploitation-with-restraint, reporting, and remediation—so you can understand what “good” looks like and how to run it safely at scale. Table of Contents What Ethical Hacking Is (and What It Is Not) Why Ethical Hacking Matters to Business Outcomes Legal and Ethical Foundations: Permission, Rules, and Boundaries Core Methodology: The Penetration Testing Lifecycle Scoping and Preparation

Read More »

Get Social

Buy The Buzzard A Coffee

Contribute